SPF record explained 

What is SPF (Sender Policy Framework)?

There are various ways that cyber-criminals can forge emails. They can modify the “Mail from” and make the emails look like they are coming from a specific domain when they are not. The SPF. Sender policy framework protocol is here to put strict rules. With SPF, the domain administrator can strictly limit who can send emails from the domain. The other part, the receiver, has a mechanism to check the authorization and take the necessary measures.

The outcome of the SPF evaluation can be:

  • None – No SPF record was found, or the record was not properly configured.
  • Neutral – The DNS admin is not stating that a particular IP address is authorized.
  • Pass – The client is authorized to inject emails with the identity provided.
  • Fail – Not authorized to use the domain.
  • Softfail – Probably not authorized. There is a stronger “Fail” missing.
  • Temperror – Currently, there is an error, most probably related to the DNS. Later, if retry again, the problem could be gone.
  • Permerror – Permanent error. The DNS admin must fix an error because otherwise, the SPF record could not be understood.

Why do you need a DNS SPF record?

Continue reading “SPF record explained “

Shared Hosting vs VPS: When Should a Website Upgrade?

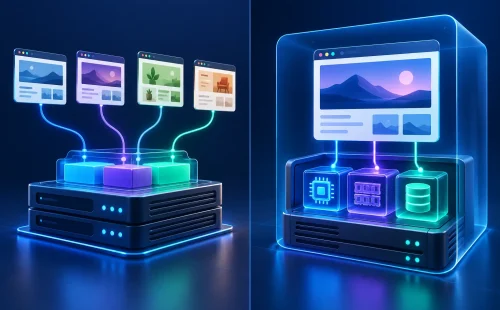
Shared hosting is an efficient starting point for many websites. It keeps cost and administration low while the provider manages most of the server. As traffic, application complexity, or business importance grows, a Virtual Private Server can offer more predictable resource limits and much greater control. The difficult part is deciding when those benefits justify the added cost and responsibility.

The right choice depends on workload rather than prestige. A well-optimized brochure site may run comfortably on shared hosting for years, while a busy store, membership platform, or custom application can outgrow it quickly. This comparison explains the practical differences and the signals that indicate an upgrade is likely to solve a real problem.

If you are selecting a first plan rather than considering an upgrade, begin with the broader guide to web hosting for small businesses. It covers the baseline questions that should be settled before comparing server models.

How shared hosting works

On a shared hosting plan, many customer accounts use the same underlying server and operating environment. The provider divides storage, processing time, memory, and other resources through account limits. Customers usually receive a control panel, website and database tools, email features, backups, and managed server maintenance without root-level access.

This model is attractive because setup is simple and the provider handles operating-system updates, core services, hardware failures, and much of the platform security. It often suits portfolios, small company sites, blogs, landing pages, and other projects with moderate resource needs.

The compromise is limited control. You normally cannot replace the operating system, install arbitrary system services, or tune every web-server parameter. Other accounts share the same physical resources, and provider limits may constrain CPU time, memory, processes, database activity, or simultaneous requests during traffic spikes.

How VPS hosting works

A VPS uses virtualization to create isolated server environments on physical hardware. Each virtual server runs its own operating system and has defined allocations or limits for CPU, memory, storage, and network usage. The exact guarantees vary: memory may be fixed, while CPU capacity can still involve contention unless the provider explicitly offers dedicated cores or stronger reservations.

A VPS usually allows administrators to select the software stack, configure the firewall, create system users, adjust services, schedule background jobs, and install application dependencies. That flexibility is valuable for custom applications, stores, high-traffic sites, development environments, and workloads that need specific versions or server modules.

For another concise comparison of the two models, see Shared Hosting vs VPS. The key point is that VPS hosting provides a separate administrative environment, but it does not automatically make an unoptimized website fast or secure.

Shared hosting vs VPS: the important differences

Performance and resource consistency

Shared hosting can perform very well for a lightweight, cacheable website. Providers often optimize the common stack and spread maintenance costs across many users. Performance becomes less predictable when an account reaches plan limits, runs expensive database queries, or competes for shared capacity during busy periods.

A suitably sized VPS provides clearer resource boundaries and more tuning options. You can adjust the web server, runtime workers, database buffers, caching, and background processes for the application. Results still depend on virtualization quality, storage, network capacity, server configuration, and the software itself.

Control and software flexibility

Shared hosting offers a curated environment. That reduces administrative work but restricts custom packages, ports, services, and system-level settings. A VPS offers root or administrator access, allowing a tailored stack and deployment workflow.

More control also means more ways to create an outage. A bad firewall rule, unsafe package source, full disk, expired certificate, or incorrect service configuration can take the site offline. Choose a managed VPS if the organization needs VPS resources but does not have the time or expertise to maintain the operating system.

Security responsibilities

On shared hosting, the provider secures and patches the base platform. Customers remain responsible for application updates, passwords, permissions, themes, plugins, and stored data. Account isolation is critical because many sites share the server.

A VPS provides stronger environment separation and the ability to enforce custom controls, but an unmanaged VPS moves more security work to the customer. That includes operating-system patches, SSH hardening, firewall policy, malware response, service exposure, log review, backups, and vulnerability management. Isolation is useful only when the virtual server is maintained correctly.

Cost and operational effort

Shared plans are generally cheaper because infrastructure and administration are distributed across many accounts. A VPS costs more and may add expenses for a control panel, backup storage, monitoring, security tools, licenses, and management services.

Include staff time in the comparison. An inexpensive unmanaged VPS can become costly if troubleshooting consumes hours or if a configuration mistake causes downtime. Conversely, staying on an undersized shared plan may cost more through slow checkouts, failed background jobs, or lost visitors.

Match the hosting model to the website

Website architecture changes the resource profile. A mostly static site can be served efficiently with modest processing, while a dynamic site may run application code and database queries for each uncached request. The guide to static vs dynamic websites explains these architectural differences.

Shared hosting is often sufficient when the site:

  • has moderate and predictable traffic;
  • uses a conventional CMS and supported extensions;
  • fits comfortably within storage, memory, CPU, and process limits;
  • does not need custom system services or unusual runtime versions;
  • benefits more from provider management than from root access.

A VPS becomes more appropriate when the site or application:

  • regularly reaches documented account limits;
  • needs predictable capacity for traffic peaks, transactions, or scheduled tasks;
  • requires custom packages, services, ports, or server configuration;
  • runs several applications that need isolated resources and deployment control;
  • has monitoring, logging, firewall, or compliance requirements unavailable on the shared plan.

Signs that it may be time to upgrade

Resource-limit events are frequent

Review the hosting control panel and support records for CPU throttling, memory exhaustion, process limits, database connection limits, and storage I/O restrictions. A single peak does not justify migration, but repeated limit events during normal operation indicate a capacity mismatch.

Performance remains poor after application optimization

Measure response time and identify whether delays come from the application, database, external services, or server limits. Optimize images, queries, plugins, themes, caching, and frontend assets first. For WordPress, the existing overview of caching plugins illustrates one application-level technique.

If the application is reasonably optimized and still experiences CPU queues, slow database work, or insufficient memory, a VPS can provide the headroom and tuning access needed for the next stage.

The project needs unsupported software

A custom worker, queue, search service, runtime extension, proxy, or deployment agent may not be permitted on shared hosting. Moving is reasonable when the requirement is essential and cannot be met through the existing control panel or a suitable managed service.

Business risk has increased

An online store, subscription service, or customer portal may justify stronger monitoring, isolated staging, controlled deployments, and documented recovery even before it exhausts resources. The decision should reflect revenue impact and recovery objectives, not traffic alone.

What a VPS will not fix automatically

More resources do not repair inefficient database queries, oversized media, broken plugins, excessive third-party scripts, memory leaks, or poor cache strategy. A VPS also does not provide backups, security monitoring, or high availability unless those features are configured or included in a managed plan.

Before migrating, establish a baseline: page response time, CPU and memory usage, database latency, error rate, traffic pattern, storage growth, and backup duration. After migration, repeat the same measurements. Without a baseline, it is difficult to know whether the move addressed the bottleneck.

A practical migration checklist

  1. Choose managed or unmanaged service. Assign responsibility for patches, monitoring, backups, incidents, and support.
  2. Size from evidence. Use current usage and peak behavior to estimate CPU, memory, storage, and data-transfer needs.
  3. Build the server securely. Install supported software, restrict administrative access, configure a firewall, and enable monitoring.
  4. Create independent backups. Test a restore before changing production DNS.
  5. Migrate to a test address. Validate pages, forms, email delivery, scheduled jobs, uploads, redirects, certificates, and database writes.
  6. Plan the DNS change. Lower TTL in advance when appropriate, preserve the old environment during verification, and monitor both systems.
  7. Measure after launch. Compare the new environment with the baseline and tune based on observed bottlenecks.

If the site uses WordPress, confirm that the new environment meets the current official WordPress requirements and uses supported versions of PHP, the database, and HTTPS.

Conclusion

Shared hosting is the sensible choice when a website fits its limits and the value of provider management outweighs the need for server control. A VPS is justified when measured resource pressure, custom software, operational requirements, or business risk demand a more isolated and configurable environment. Optimize first, size from evidence, and include management and security work in the true cost of the upgrade.
Static vs Dynamic Websites: Which Architecture Fits Your Project?

Every website ultimately sends HTML, CSS, images, and scripts to a browser, but the way those files are created can be very different. A static site usually serves prepared files directly. A dynamic site generates or assembles a response with application logic, content systems, databases, or external services.

Neither architecture is automatically better. The right choice depends on how often content changes, who must edit it, whether visitors need personalized features, how much operational complexity the team can support, and what the hosting environment needs to provide.

What is a static website?

A static website stores ready-to-deliver files. When a visitor requests a page, the web server or edge cache returns the existing HTML and related assets without building the page from a database for that request.

“Static” does not mean visually plain or completely non-interactive. A static page can use responsive design, animations, client-side JavaScript, forms connected to external services, search tools, and APIs. The defining characteristic is that the main page content is prepared before the request rather than generated by server-side application code on every visit.

Typical static-site workflow

  1. Content and templates are stored in files or a content system.
  2. A build process creates the final HTML, CSS, JavaScript, and media assets.
  3. The generated files are deployed to a web server, object storage, or content delivery network.
  4. Visitors receive the same prepared version until a new build is deployed.

What is a dynamic website?

A dynamic website uses server-side processing to create or assemble content when it is requested, or it loads data through application interfaces after the initial page arrives. The response may depend on a database, an authenticated account, inventory, visitor permissions, form input, location, or other current information.

Content management systems, online stores, customer portals, forums, booking systems, and software dashboards commonly use dynamic components. A WordPress site, for example, typically retrieves posts and settings from a database and renders them through a theme, although caching can store the resulting pages to avoid repeating all work for every visitor.

How hosting requirements differ

Static files can be served by a simple web server or distributed through edge storage and a CDN. The origin does not need a database or a server-side application runtime merely to deliver prepared pages. This can make deployments predictable and reduce the number of moving parts.

Dynamic sites normally need a compatible runtime, database access, memory and CPU for application work, secure secrets, backups, monitoring, and an update process. Some platforms manage much of that infrastructure, while traditional hosting gives the site owner more direct responsibility.

The hosting layer matters for both models. A clear introduction to domains, servers, and hosting resources is available in What Is Web Hosting and How Does It Work?. This external reference appears here in the first half because hosting is one of the earliest architectural decisions.

The existing guide to choosing web hosting for a small business also provides useful evaluation criteria. A static site may fit a lightweight plan, while a busy dynamic application may require isolated resources, database tuning, or a scalable platform.

Static website advantages

Fast and cache-friendly delivery

Prepared files are easy to cache close to visitors. There is little server-side work between the request and the response, so a well-built static site can provide consistent performance under varying traffic.

Smaller operational surface

Without a public database connection, application runtime, or administrative dashboard in the delivery path, there are fewer components to configure, update, and monitor. The deployment still needs secure access and correct headers, but the architecture can be simpler.

Predictable deployments

A build creates a known set of files that can be reviewed and tested before publication. Rollback can be as simple as restoring an earlier deployment when the hosting platform supports versioned releases.

Efficient handling of traffic spikes

Static assets can be replicated and cached widely. A sudden increase in page views is less likely to create database contention or exhaust application workers.

Static website limitations

  • Publishing may require a rebuild. Large sites can need careful build optimization and incremental publishing.
  • Personalized server-side features require extra services. Accounts, live inventory, and complex transactions cannot be implemented with files alone.
  • Editorial workflows vary. Non-technical editors may need a headless CMS or a purpose-built interface rather than editing files.
  • Freshness depends on deployment. Data can become stale if the build or content synchronization process fails.

Dynamic website advantages

Personalization and permissions

Dynamic logic can show account-specific information, enforce roles, maintain sessions, and adapt content to current application state.

Immediate content updates

A CMS can publish an update to the database without rebuilding an entire site. Editors can use familiar administrative workflows, revisions, scheduled publishing, and media libraries.

Complex transactions

Shopping carts, reservations, payments, search indexes, dashboards, and user-generated content depend on current server-side data and validation.

Integration with business systems

Dynamic applications can coordinate with inventory, customer relationship systems, analytics, identity providers, and internal APIs.

Dynamic website tradeoffs

  • More infrastructure: application servers, databases, queues, caches, and scheduled tasks introduce dependencies.
  • More maintenance: runtimes, frameworks, plugins, and database engines require updates and compatibility testing.
  • Performance needs active design: inefficient queries or insufficient caching can slow every request.
  • A larger security surface: login systems, forms, APIs, and administrative tools require access control, validation, monitoring, and patching.

For WordPress specifically, page caching can reduce repeated server-side work. The article about caching plugins for WordPress explains one way dynamic platforms improve delivery performance.

A side-by-side comparison

Decision area Static approach Dynamic approach
Page creation Before deployment At request time or through live data calls
Hosting Files, web server, or CDN Runtime, database, and application services
Content updates Usually rebuild and deploy Often publish through a CMS or application
Personalization Limited without external services Built around users, sessions, and live data
Maintenance Generally fewer server components More software and dependencies to operate
Traffic spikes Highly cacheable Requires caching and capacity planning

Hybrid architecture: using both models

Many modern sites are neither fully static nor fully dynamic. A team may prebuild public marketing pages while keeping account areas, checkout, search, and live inventory dynamic. Another project may serve static HTML and fetch current information from an API in the browser.

Platform-as-a-service products can host application components without requiring a team to manage every server directly. The overview What is PaaS? describes that hosting model. Static generation and managed application services can also be combined within one project.

How to choose the right architecture

  1. List the required interactions. Separate ordinary content pages from accounts, payments, live search, and transactions.
  2. Map the publishing workflow. Identify who creates content, how often it changes, and whether updates must appear immediately.
  3. Estimate traffic and performance needs. Consider geographic distribution, cacheability, peak usage, and the cost of server-side work.
  4. Assess operational capacity. Choose an architecture the team can secure, monitor, update, back up, and restore.
  5. Plan for failure. Decide what happens when the database, build system, API, or hosting region is unavailable.
  6. Use a hybrid when boundaries are clear. Keep content static where possible and add dynamic services where they deliver real value.

Conclusion

Static websites are strong when content can be prepared ahead of time and served efficiently with minimal infrastructure. Dynamic websites are appropriate when visitors need accounts, transactions, personalization, or frequently changing server-side data. A hybrid architecture often offers the best balance by keeping public content cacheable and isolating truly dynamic features.

For a standards-oriented introduction to server-side website programming and the distinction between static and dynamic behavior, see MDN’s introduction to server-side websites.

Why GeoDNS Is Essential For Your Success?

Do you want to learn what the purpose of GeoDNS is? Great!! You are on the right article because we will exactly explore this. Additionally, we will explain for who GeoDNS is advantageous and how to make the comparison between Anycast and GeoDNS. Finally, we will see about the thing you need to think about before paying for it. 

What does GeoDNS imply?

The Geographical Domain Name System, often known as GeoDNS, is an effective method of traffic allocation. It works by responding to queries based on their location. Additionally, it can be seen as a local or worldwide traffic director.

GeoDNS is a robust load balancing solution that optimizes traffic to domains. Utilizing it lessens issues and fortifies networks.

Continue reading “Why GeoDNS Is Essential For Your Success?”

User Datagram Protocol – What is it?

User Datagram Protocol, or simply UDP, is one of the most essential components of the Internet Protocol Suite. It is a collection of Internet-related network protocols. But how does it work, and when do we use it? We will take a detailed look at this point in today’s article.

User Datagram Protocol – detailed explanation

The User Datagram Protocol (UDP) is a well-known high-speed communications protocol. It’s what we employ to make low-latency, loss-tolerant connections between various Internet services.

The User Datagram Protocol allows data to be transferred before the recipient agrees, which speeds up the communication process. As a result, UDP is the preferred method for time-sensitive communications such as DNS lookups, Voice over IP (VoIP), video, or audio transfers.

History of UDP

Continue reading “User Datagram Protocol – What is it?”

A record and PTR record: What are the differences?

A record and PTR record are an essential part of the Domain Name System process. They appear to be similar at first look, but they are actually quite different. In today’s article, we’ll look at the characteristics of both records and how they differ.

A record – meaning

The A record, also known as the address record, is one of the essential DNS records. It uses a domain name to find the device’s IP address connected to the Internet. As a result, every time a user types in their browser and wants to visit a specific website, they will require the A record. Thanks to that, it is going to be able to reach it. 

What is a DNS record and why is it important?

Continue reading “A record and PTR record: What are the differences?”

IPAM: Explained

Have you ever wondered how every device is looking for an Internet connection? And they are so many! This happens daily and all around the world. With the growing number of laptops, smartphones, tablets, and other devices, network management is becoming very complex.

Imagine how time-consuming it is to assign IP addresses or to track them. And network administrators have so many more responsibilities to comply with. It is not a choice to do this manually. In that case, IP address management (IPAM) is very beneficial.

Why is IPAM important?

Continue reading “IPAM: Explained”

How does rDNS (Reverse DNS) work?

After you set up your Forward DNS and add your DNS records, it is a great idea to set up a rDNS (Reverse DNS)! When you try to send an email from the domain, you will probably notice a problem. Your emails will go missing or to the SPAM folder. And this is something nobody wants for their business. So, now let’s explain a little bit more about rDNS (Reverse DNS).

What is rDNS?

Reverse DNS is also known as rDNS. It has the opposite purpose to a Forward DNS, which is to map IP addresses to hostnames. The main reason for using the Reverse DNS is to implement a way to verify the IP addresses and prove that they are related to a particular domain name. It is mainly necessary when we are talking about the verification of mail servers or other services. 

Continue reading “How does rDNS (Reverse DNS) work?”

What is a DNS TXT record?

What is a TXT record?

The TXT record is a type of DNS record that has TXT-DATA filed with instructions that can work with existing DNS servers. The actual text is formatted, so it has an attribute name than a value for that attribute, and the “=” sign separates the two. The most common way of TXT record use is for email verification, but it also servers for various verification and authentication methods. Some services (Google Apps, Microsoft Office 365, and more) will ask you to add such a DNS record to your zone to prove that you have control over your domain.

How does TXT records work?

Continue reading “What is a DNS TXT record?”

DNS load balancing: What is It and Why Do You Need It?

What is DNS load balancing all about? Well, the fact is that you can’t allow a web server to overload. If your business website has a slow and faulty network, it will definitely impact the end-user experience. It will cause poor perception of the site and so on to your organization. 

Therefore it is important to implement a load balancing method when you are managing your network.

What is DNS load balancing?

DNS load balancing is a technique for administrating the traffic of a hostname. It is about troubleshooting the distribution of inbound network and application traffic across multiple servers.

Websites with a lot of traffic are operating with many requests from users or clients. For every request, they have to return the exact and correct text, images, video, or application data, all in a fast and safe way.

DNS load balancers are intelligent. First, they use various criteria and examine the traffic. Next, they decide to let the traffic proceed or stop it and redirect it to a different server based on the current packet load or another parameter. 

Complete comparison between DNS load balancing and Hardware load balancing

Continue reading “DNS load balancing: What is It and Why Do You Need It?”

How does Anycast DNS work?

The Domain Name System (DNS) is one of the foundations of the Internet, yet most people outside of networking probably don’t realize they use it every day to do their jobs or check their email. Anycast DNS helps using the Internet to be even faster and efficient. Let’s talk about that a little bit more.

What is Anycast DNS?

When you choose Anycast DNS as your routing method, you can establish your IP address in several DNS servers.

Through Anycast, different servers positioned in many geographical locations are capable of answering the query. The closest of them will provide the IP address to the user. 

Also, if one of the DNS servers is down for some reason, the second closest server will receive the request. 

Experience is faster and better with Anycast DNS when we speak about loading time, waiting for a response, etc.

Before we continue, let’s explain a little bit more about what DNS is.

Continue reading “How does Anycast DNS work?”